Inclave Login: How One Account Works Across Casino Sites
 Available in AU
Shared account access
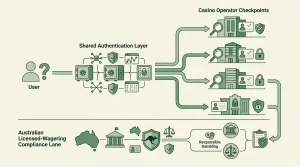
Inclave login is a shared authentication model used by supported casino sites. One Inclave account can be recognised across participating brands, but the casinos do not become one combined gambling account. Balances, bonus terms, game libraries, cashier functions, withdrawals, licensing and casino-level verification remain separate. Inclave also supports biometric login on compatible devices and can be used across compatible desktop and mobile browsers.
Table of Contents
- How the shared Inclave login works
- A high-level Inclave login flow
- What is shared and what stays separate
- Biometric login on compatible devices
- Cross-device access without a shared casino wallet
- What one Inclave login does not combine
- Registration intent belongs with login, not with casino economics
- Moving from one supported casino to another
- KYC can still happen after the shared login
- Why login convenience is not an operator trust score
- How this fits the broader Inclave model
- When the login page is not enough to answer the question
- Current references for Inclave login
- Using one Inclave login without confusing separate casino accounts
- Inclave Login: How One Account Works Across Casino Sites
How the shared Inclave login works
The core idea is single sign-on across supported casino brands. Instead of treating every participating site as a completely separate identity system, an Inclave account can be recognised by more than one connected casino. The shared part is authentication. The gambling account behind that authentication remains specific to the casino you are visiting.
That means the same identity can help you access another supported site, but it does not carry a shared balance, bonus entitlement or universal cashier with it. The operator still controls the casino-specific account.
A high-level Inclave login flow
The verified model can be understood in four stages without relying on unsupported password-recovery or device-reset instructions.
Use a supported casino
The casino must have integrated Inclave. The shared-login model does not apply to unrelated sites.
Use the Inclave identity layer
The account is authenticated through Inclave rather than being treated as a completely separate identity at every connected brand.
Authenticate on a compatible device
Inclave supports biometric authentication such as facial or fingerprint login where the device and implementation support it.
Enter the casino’s separate account environment
The casino recognises the authenticated user, but its own balance, games, promotions and cashier remain under that operator.
This is intentionally a high-level flow. Exact recovery, reset or device-change procedures can change and should be followed from the current Inclave interface rather than copied from an old third-party tutorial.
What is shared and what stays separate
Shared login can make account access feel unified, but the underlying casino relationships are still separate. The table below shows the boundary that matters most.
| Account element | Shared through Inclave? | What to expect |
|---|---|---|
| Identity/login layer | Yes, across supported brands. | One Inclave account can be recognised at multiple connected casinos. |
| Biometric authentication | Supported on compatible devices. | Facial or fingerprint login can be available as an authentication method. |
| Casino balance | No. | Each casino controls and holds its own gambling balance. |
| Bonuses | No. | Promotion terms are created by the individual casino operator. |
| Games | No. | Each operator chooses its own game library and providers. |
| Cashier and withdrawals | No. | Deposits, withdrawals and payment processing belong to the casino. |
| Casino licence | No. | Licensing is tied to the gambling operator, not to the shared login. |
Biometric login on compatible devices
Current Inclave-related sources describe biometric authentication such as facial recognition or fingerprint login. This can reduce repeated typing during sign-in, but the wording needs to stay precise: biometrics are supported on compatible devices rather than guaranteed on every browser, phone or desktop setup.
Biometric authentication also does not change the operator boundary. A fingerprint or face check can help authenticate the user, but it does not authorise a casino’s bonus terms, move money between casinos or verify that a connected operator has a particular gambling licence.
For device-specific considerations, see the separate mobile and biometric login.
Cross-device access without a shared casino wallet
Inclave account access is described as compatible across desktop and mobile browsers and devices. That is useful when a player moves between a computer and a phone, but cross-device identity should not be confused with a cross-casino wallet.
The financial relationship still sits with each operator. If you deposit at Casino A, the existence of the same Inclave identity at Casino B does not mean the funds become available at Casino B. The same separation applies to withdrawal histories, payment methods and transaction limits.
This distinction is one of the most important checks when reading claims about “one Inclave account”. It means one reusable identity for supported sites, not one pooled gambling balance.
What one Inclave login does not combine
Balances
Each casino keeps its own player balance. Money does not become part of a network-wide Inclave wallet.
Bonus terms
A promotion at one casino does not create an Inclave-wide offer or entitlement at another site.
Game libraries
Slots, table games and live titles are selected by each operator, not by the login layer.
Legal status
A shared login does not determine whether the gambling service is authorised or suitable for Australian users.
KYC requirements
Casino-level verification can still vary by operator and should not be treated as one universal Inclave checklist.
Withdrawals
The casino that operates the cashier controls payout processing, not Inclave.
Registration intent belongs with login, not with casino economics
Users searching for “Inclave sign up” are usually trying to solve an access problem: how to create or use the identity that a participating casino recognises. That is different from deciding whether the casino itself is suitable. The shared login can answer the first question, while the operator’s own terms, licence information and cashier answer the second.
For that reason, this guide does not attach a universal minimum deposit, bonus amount or payment method to the registration process. Those are operator-specific details and can differ between connected casinos even when both use the same Inclave identity layer.
Moving from one supported casino to another
The practical value of a shared identity becomes clearer when more than one participating brand recognises the same Inclave account. The user does not need to think of the second site as part of one combined casino. Instead, the same authentication identity is being accepted by another operator that still maintains its own gambling environment.
This matters when comparing what happens immediately after sign-in. The second casino can show a different lobby, different promotions and a different cashier because those parts are not inherited from the first operator. The common login reduces identity repetition; it does not standardise the rest of the experience.
For an Australian reader, this is also a useful due-diligence rule. Recognition of the same Inclave account is not proof that both casinos have the same licensing position, country access or account terms. Those checks still need to be made against each operator separately.
KYC can still happen after the shared login
A working Inclave login does not mean every casino-level verification requirement has been completed. Connected casinos can still apply their own KYC checks. The exact documents, timing and transaction triggers should be taken from the current operator policy rather than treated as a fixed Inclave-wide process.
The useful distinction is that authentication proves access to the identity used for sign-in, while operator KYC addresses the casino account and its transactions. The separate KYC and verification explains that boundary in more detail.
Why login convenience is not an operator trust score
A shared sign-in system can make access simpler, but it does not tell you how a casino handles withdrawals, complaints, game selection or customer support. Those outcomes depend on the operator behind the site.
When evaluating a connected casino, first identify the operator and then review the operator’s own evidence. The broader Inclave review keeps the authentication layer separate from the gambling service so that one does not become a proxy for the other.
How this fits the broader Inclave model
If the difference between identity and casino operation still feels abstract, the what Inclave is maps the responsibilities side by side. The main point for login is simple: Inclave can be the common door, while each casino remains a separate room with its own rules, money and products.
That model is also why a list of casinos that support Inclave should not be read as a list of casinos with identical terms. The authentication connection is the common feature. Everything else needs to be checked at operator level.
When the login page is not enough to answer the question
Some questions that look like login questions are really operator questions. If the issue is a missing withdrawal, a bonus condition, an unavailable game or a request for casino verification documents, the shared login page cannot supply the final answer. The relevant evidence is the casino’s own current account, cashier or terms information.
Keeping that escalation path clear prevents a technical access issue from being mixed with a financial or regulatory issue. Use Inclave information for authentication and supported access. Use casino and regulator information for the operator-specific decision.
Current references for Inclave login
Current Inclave public material describes shared account access across connected brands and keeps casino balances and cashier functions separate. Connected operator material also describes biometric login and cross-device compatibility. See Inclave’s public login explainer and the Lucky Legends Inclave integration page.
Related context: Inclave Australia guide.
Using one Inclave login without confusing separate casino accounts
Treat the Inclave account as the reusable authentication layer. Treat each connected casino as a separate gambling account with its own balance, promotions, games, cashier, verification process and licensing position. That mental model makes the shared-login benefit clear without turning it into claims that belong to the operator.